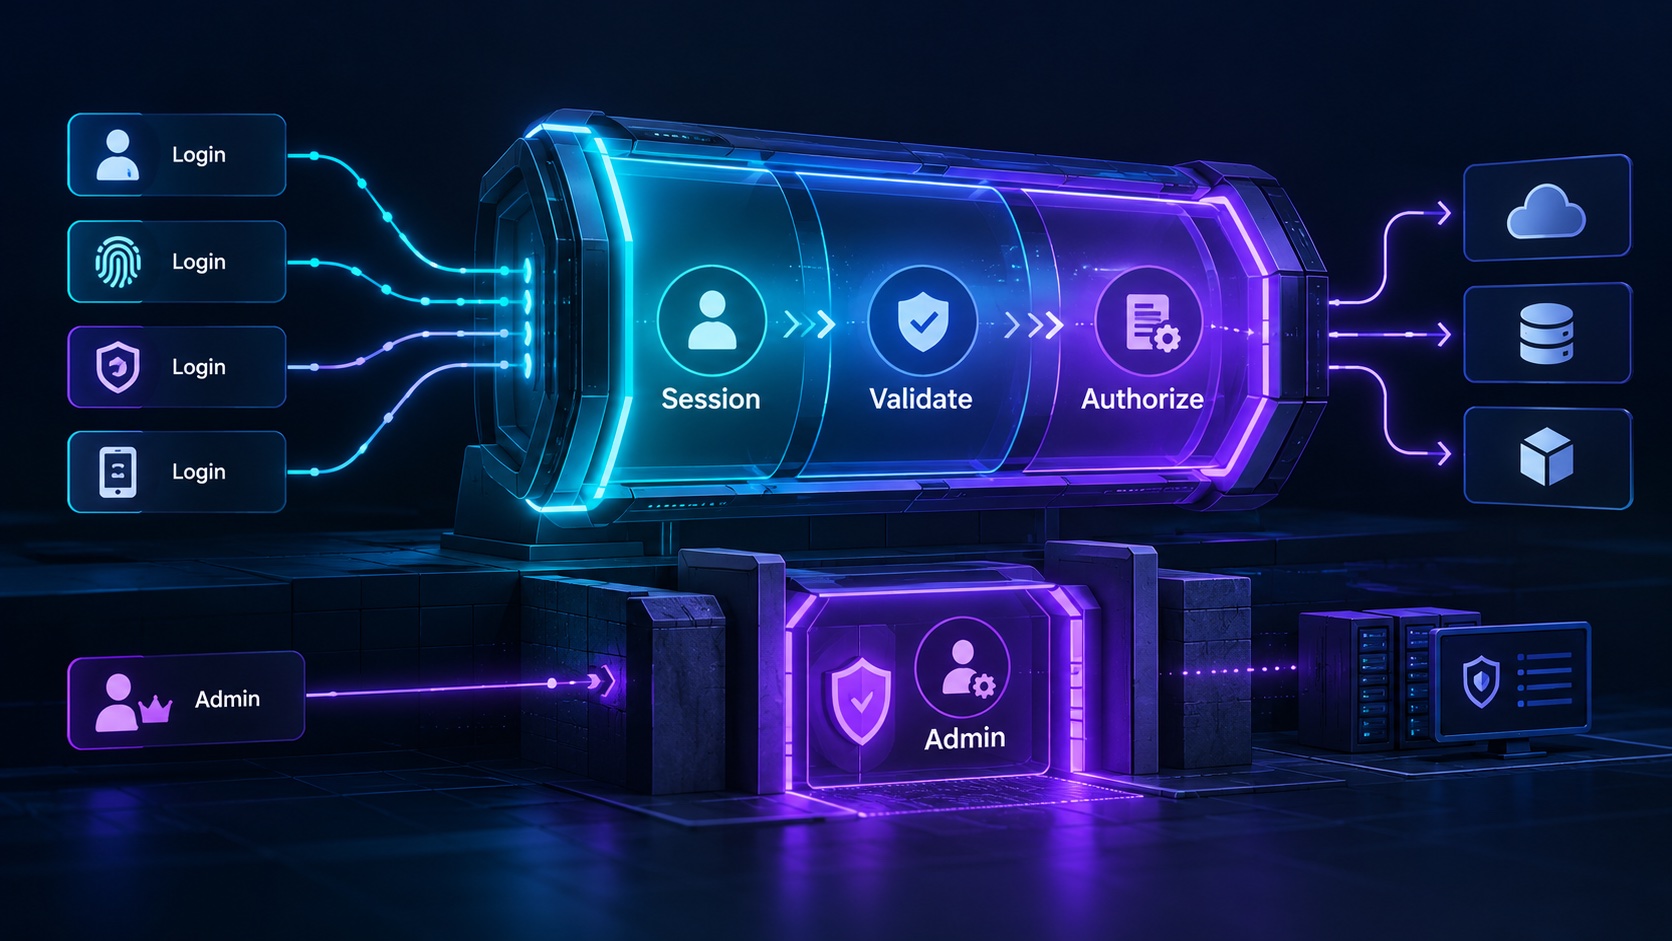
Authentication establishes a user's identity. In a SaaS application, it must work reliably with sessions, protected routes, account recovery, workspace membership, and authorization.
Choose Supported Login Methods
Depending on your audience, you may need social login, email magic links, or password-based authentication. Select methods based on usability, security, and operational requirements.
Manage Sessions Carefully
Define how sessions are created, expired, invalidated, and refreshed. Consider what should happen when a user loses access to an account or an administrator revokes permissions.
Separate Authentication From Authorization
Knowing who a user is does not establish which data they may access. Check permissions on every protected operation.
Protect Administrative Access
Administrative accounts should be provisioned deliberately, with clear controls over who can receive elevated privileges.
Test Security Boundaries
Test expired sessions, unauthorized requests, invalid callbacks, and attempts to access another user's data.
Conclusion
A secure authentication system is part of a broader identity and access-control design.
Agentium Start documents Google, Apple, and GitHub OAuth, magic-link email login, database sessions, route protection, and RBAC in its current feature inventory. Verify the supported scope against your application's requirements before implementation.