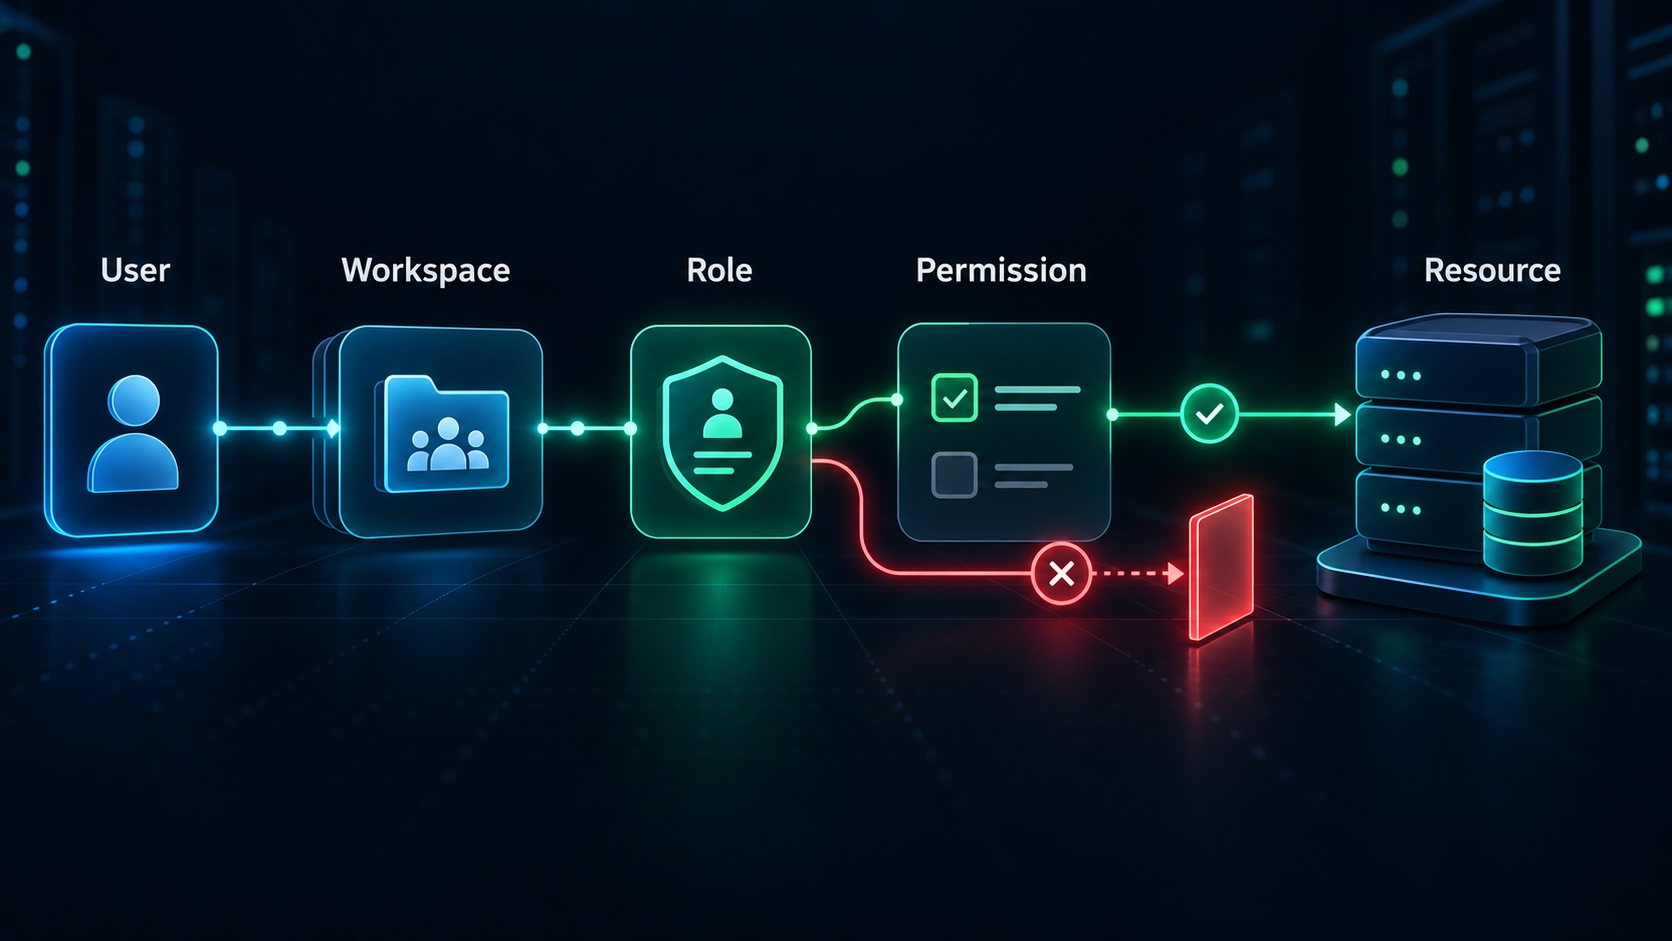
Role-based access control, or RBAC, determines which actions users can perform based on their assigned roles. It is especially important in B2B applications where administrators, managers, and members need different levels of access.
Define Roles and Permissions
Start by listing protected actions such as inviting members, changing billing details, managing projects, and modifying workspace settings.
Map each action to the roles permitted to perform it.
Scope Roles Correctly
In multi-tenant applications, a user's permissions may differ between organizations. A person can be an administrator in one workspace and a regular member in another.
Avoid relying on a single global role when permissions depend on workspace membership.
Enforce Permissions on the Server
Frontend controls improve usability but do not provide security. Every protected operation must independently validate the user's identity and permissions.
Avoid Excessive Complexity
Begin with a small, understandable role model. Add fine-grained permissions when business requirements justify them.
Test Authorization
Verify that unauthorized users cannot access restricted pages, APIs, or resources. Include tests for users who belong to multiple workspaces.
Conclusion
A well-designed RBAC implementation improves security and makes collaboration easier to manage.
Agentium Start includes a role-based access control foundation, workspace memberships, and a permission registry. Explore the features page to review the documented scope.